An independent project exploring how to authorize concrete agent actions before execution. The current public implementation is a Java core, with transport adapters and additional modules planned.
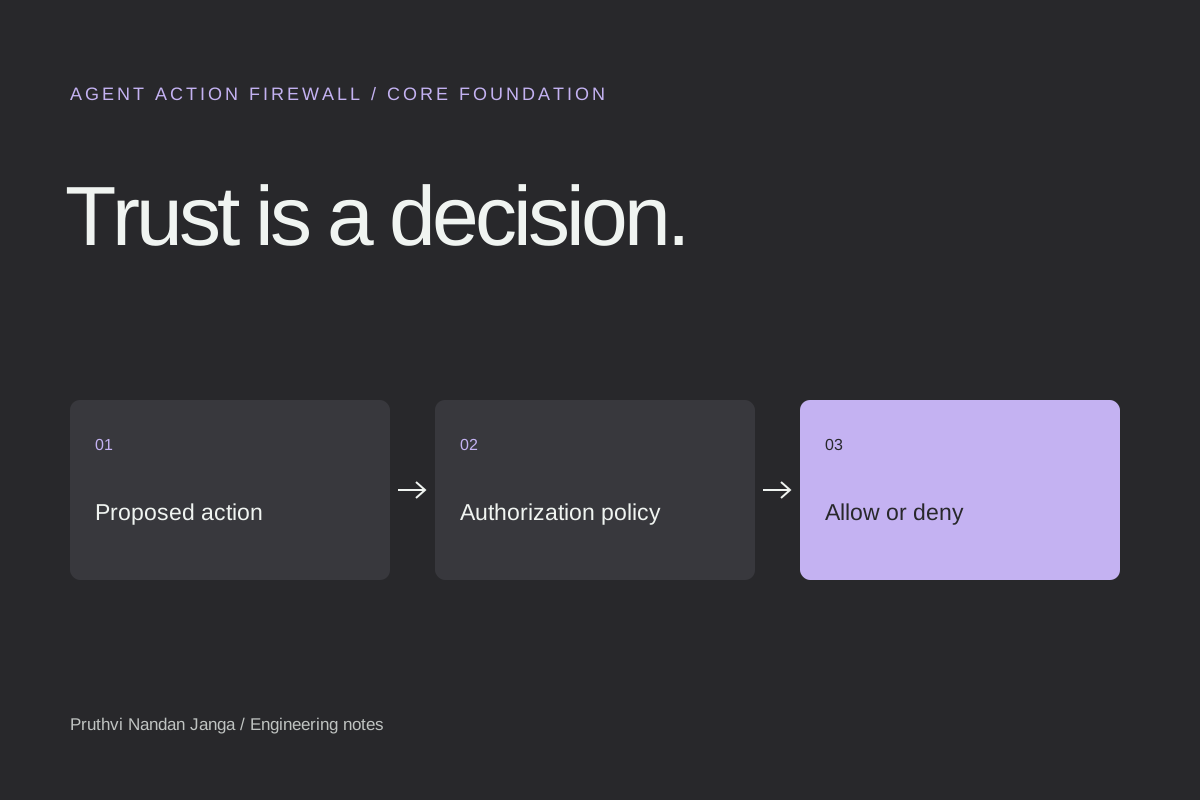
Actions are bound to canonical request digests and checked against authorization, workload identity, and policy constraints. Sanitized decision traces explain the outcome.
Implemented foundation
Framework-neutral authorization engine boundary, canonical HTTP and MCP action models, redacted credentials, and replay-protection interfaces.
Design choice
Keep transport and authorization engines replaceable. When authorization cannot be established, deny the action.
Current scope
Core foundation in progress. Gateway integration, persistent trace storage, and a complete attack runner are roadmap items, not shipped features.